GuidehouseGuidehouse
Guidehouse
  • Industries
    All Industries
    Industries
    • Communities, Energy & Infrastructure
    • Defense & Security
    • Financial Services
    • Health
    • State & Local Government
    Europe, Middle East & Canada

    Europe, Middle East & CanadaShaping industries with global scale

  • Services
    All Services
    Services
    • AI & Data
    • Energy & Resilience
    • Finance & Revenue
    • Managed Services
    • Mission Enablement
    • Operations & Efficiency
    • People, Organization & Change
    • Risk, Regulatory & Compliance
    • Technology
  • Insights
    All Insights
    Insights
    2026 Trends Guide
    • Energy Providers
    • Government Agencies
    • Financial Services
    • Health
    featured content

    The GuideLine podcast: Finding balance through fast tech and high stakes

  • Careers
    All Careers
    Careers
    • Early Career
    • Contractors
    • Experienced Professionals
    • Veterans & Military
    Help Guide the Future

    Search & Apply for Jobs

  • About
    About Guidehouse
    About
    • Community Impact
    • Government Contract Vehicles
    • D.C. United Partnership
    • Ecosystem Partners
    • Europe, Middle East & Canada
    • Legal
    • News & Events
    • Leadership
    • Privacy Policy
    Guidehouse in
    DeutschlandIndiaLietuvaUnited KingdomView offices
Article

Weak Security Controls and Practices Exploited for Initial Access

July 07, 2022
Healthcare Cyberattacks Revenue Cycle
July 07, 2022

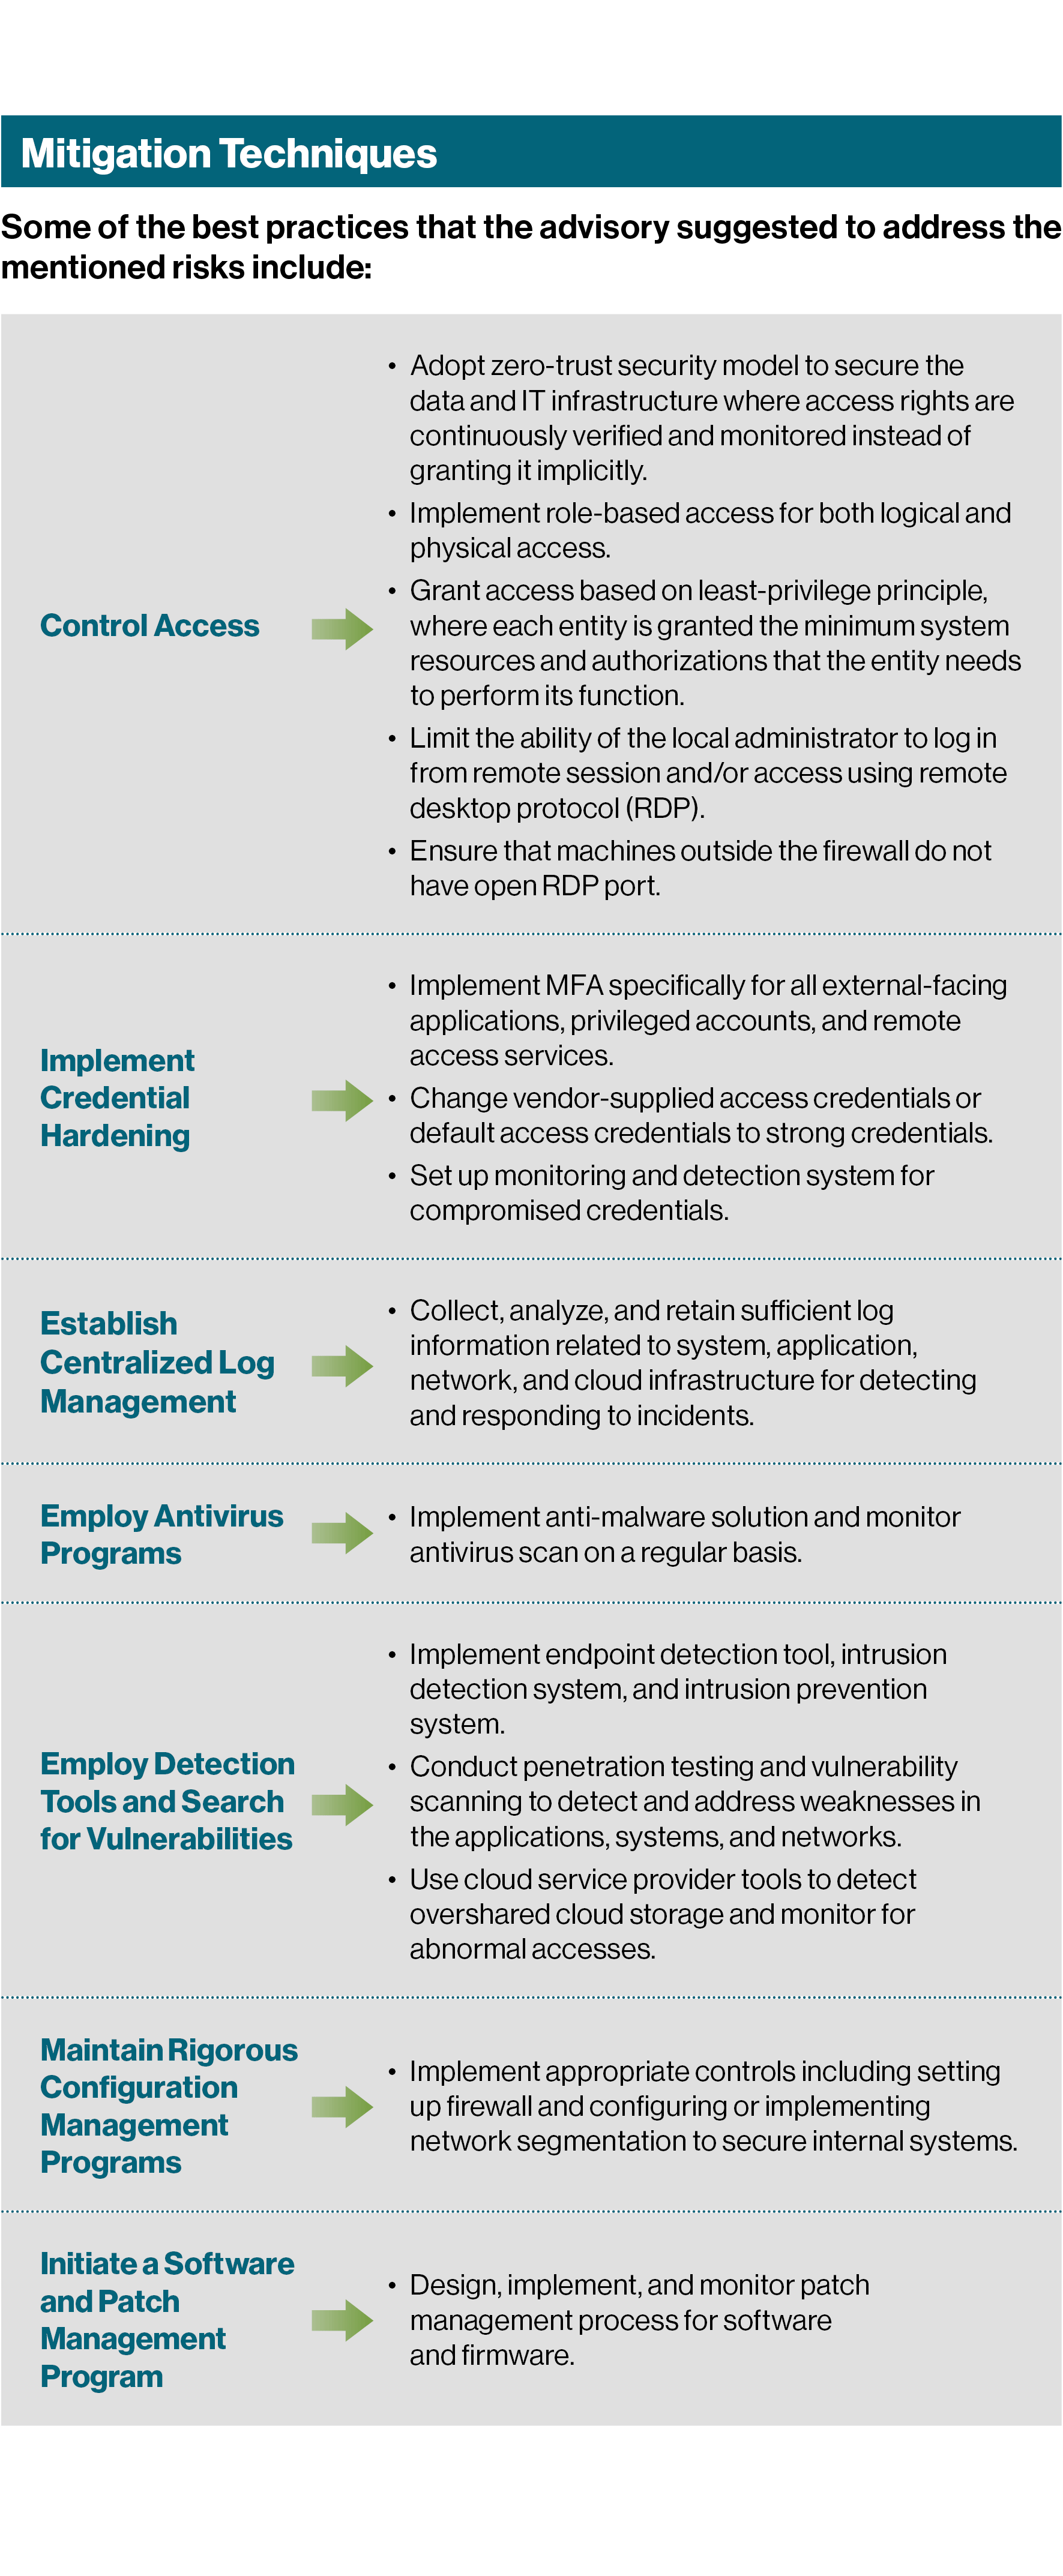
On May 17, 2022, the cybersecurity authorities1 of the United States, Canada, the Netherlands, New Zealand, and the UK published a joint cybersecurity advisory titled, “Weak Security Controls and Practices Routinely Exploited for Initial Access.”2 The advisory highlights the common techniques exploited by the malicious actors to gain initial access to the victim’s network and the common weaknesses in the control environment. Additionally, the advisory outlines some of the best practices that can be adopted to strengthen the control environment. This cybersecurity alert provides an overview of the advisory and the key areas above.


Techniques Used by Malicious Actors

The advisory stated that the common techniques used by the adversaries to gain unauthorized access to a victim’s internal environment include:

Exploit public-facing application —  An adversary can gain access by exploiting weaknesses on internet-facing applications, e.g., a design flaw in the external-facing website.

External remote services — A bad actor can use compromised credentials to gain access using remote services such as a Virtual Private Network, Citrix3, etc.

Phishing — Phishing is a technique to obtain legitimate access credentials using various methods such as social engineering or including a malicious attachment in electronic communication.

Trusted relationship — A trusted third party or service provider can have legitimate access to the victim’s system, which can be exploited by malicious actors to gain access to the internal network.


Common Weaknesses

The advisory noted that some of the most common weaknesses are:

  • Lack of enforcement of strong password and multifactor authentication (MFA) specifically for remote access
  • Errors in the access control list enabling ineligible users to get privileged access
  • Lack of patch management, allowing malicious actors to exploit known software vulnerabilities 
  • Use of vendor-supplied default configuration, creating opportunities for malicious actors to gain access 
  • Lack of controls around remote services 
  • Misconfiguration of cloud services
  • Open network ports
  • Inability to detect or block phishing attempt 
  • Lack of endpoint detection and response mechanism 
Guidehouse Service Offerings

Guidehouse has assisted numerous clients in assessing their cybersecurity and operationalizing compliance requirements using regulations, standards, and guidance issued by  authorities and global data privacy regulations. We have supported our clients by: 

  • Conducting assessments of the current state of an organization’s cybersecurity posture and developing a roadmap to achieve compliance with cybersecurity regulations and standards
  • Assisting with the implementation of a cybersecurity program that is technologically sound and sustainable, including designing and documenting policies, procedures, and control environment
  • Conducting assessment to ensure design adequacy and operating effectiveness of the cybersecurity controls
  • Designing and building cyber-resiliency program

Kathryn Rock, Partner

1. United States Cybersecurity and Infrastructure Security Agency, United States Federal Bureau of Investigation, United States National Security Agency, Canadian Centre for Cyber Security, New Zealand National Cyber Security Centre, New Zealand CERT NZ, Netherlands National Cyber Security Centre, United Kingdom National Cyber Security Centre.
2. https://www.cisa.gov/sites/default/files/publications/AA22-137A-Weak_Security_Controls_and_Practices_Routinely_Exploited_for_Initial_Access.pdf
3. Reference to specific commercial products, processes, or services by service mark, trademark, manufacturer, or otherwise does not constitute or imply endorsement and/or recommendation.

RELATED INDUSTRIES

  • Financial Services

MORE ON THIS TOPIC

  • Cyber Capability Assessment Solutions
  • New Cyber Incident Reporting Requirements for Critical Infrastructure Act and Impacts on Law Firms
  • Weather the Disruption: Business Resiliency Preparedness in a Potential Slowdown

Let us guide you

Guidehouse is a global AI-led professional services firm delivering advisory, technology, and managed services to the commercial and government sectors. With an integrated business technology approach, Guidehouse drives efficiency and resilience in the healthcare, financial services, energy, infrastructure, and national security markets.

Get in touch with our experts:

Stay ahead of the curve with our latest insights, expertly tailored to your industry.

Logo

outwit complexity™

Logo

outwit complexity™

Connect with us

Industries

  • Communities, Energy & Infrastructure
  • Defense and Security
  • Financial Services
  • Health
  • State & Local Government

Services

  • AI and Data
  • Energy & Resilience
  • Finance & Revenue
  • Managed Services
  • Mission Enablement
  • Operations
  • People Organization & Change
  • Risk, Regulatory & Compliance
  • Technology

About

  • Community Impact
  • D.C. United Program
  • Ecosystem Partners
  • General Inquiries
  • Government Contract Vehicles
  • Legal / Policies
  • Our Leadership
  • Privacy Policy
Insights
Careers
News & Events
Offices
  • Guidehouse In
  • Deutschland
  • India
  • Lithuania
  • United Kingdom
  • Privacy Notice for CA Residents
  • Modern Slavery Statement
  • Do Not Sell / Share My Personal Information
  • Cookie Settings & Do Not Sell My Personal Info
  • Global Human Rights Statement

© 2026 Guidehouse